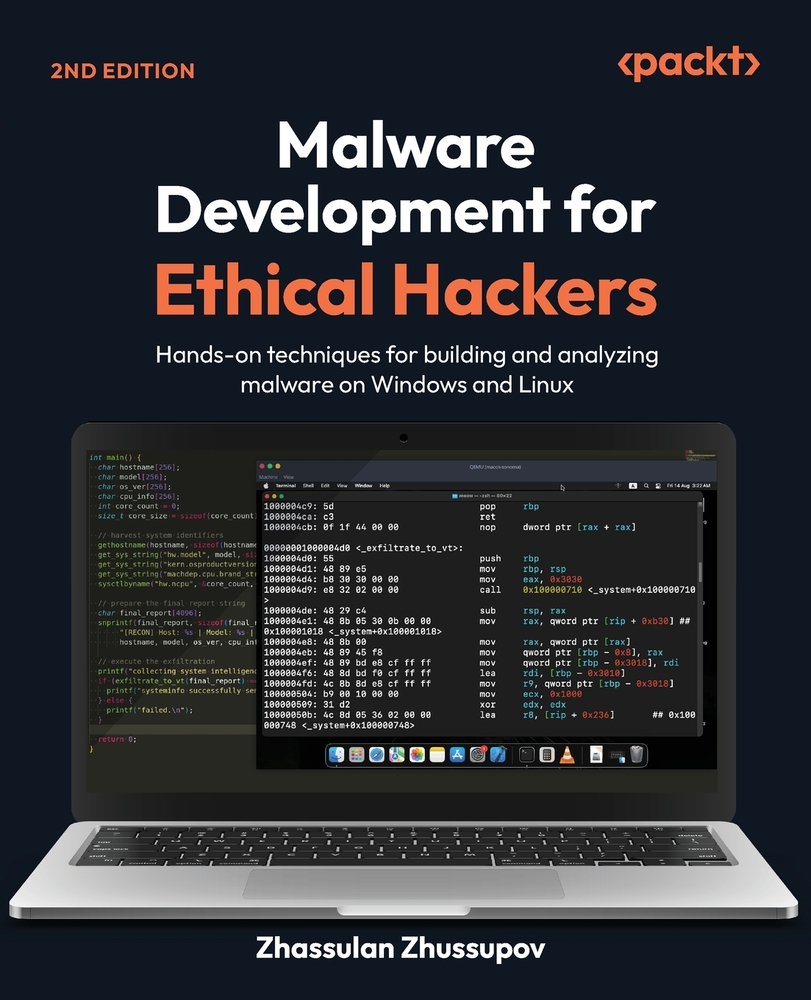
Malware Development for Ethical Hackers - Second Edition: Hands-on techniques for building and analyzing malware on Windows and Linux
In stock, ships in 1-2 business days
Free standard shipping on orders over $40. ISBN 9781807427597
About this book
Expanded to cover malware development across Windows and Linux, persistence, injection, evasion, and malware analysis, this practical, lab-based guide uses real-world examples to equip ethical hackers with hands-on skills. Key Features: - Build practical malware PoCs using C/C++ and Assembly in controlled labs - Apply red and blue team perspectives to understand malware behavior, detection opportunities, and forensic artifacts - Explore execution, injection, persistence, evasion, and anti-analysis techniques - Purchase of the print or Kindle book includes a free PDF eBook Book Description: Malware Development for Ethical Hackers, Second Edition is a practical guide to understanding how modern malware works across Windows and Linux in an ethical, research-driven context. It focuses on controlled proof-of-concept development, showing how adversaries build capabilities such as droppers, keyloggers, infostealers, loaders, persistence modules, and process injection techniques. The second edition covers malware development for Windows and Linux, with hands-on examples in C/C++ and Assembly. You'll explore execution techniques, evasion, persistence, anti-analysis, abuse of legitimate APIs, low-level system techniques, and real-world tradecraft inspired by modern APTs and malware families. The book also connects offensive development with malware analysis, detection opportunities, and forensic artifacts for security researchers and Blue Team readers. By the end of this book, you'll understand how malware is designed, executed, hidden, persisted, and analyzed across Windows and Linux. You'll be able to build safe lab PoCs, understand adversary behavior, recognize forensic artifacts, and apply this knowledge to ethical hacking, red team simulations, malware research, and practical defense. What You Will Learn: - Implement execution and injection techniques across Windows and Linux - Explore persistence mechanisms and the artifacts they leave behind - Develop practical PoCs for droppers, keyloggers, infostealers, and loaders - Study evasion, anti-analysis, and living-off-the-land techniques to understand how malware avoids detection - Reconstruct real-world adversary tradecraft for red team simulations, security research, and defensive improvement Who this book is for: This book is for penetration testers, red team engineers, malware researchers, exploit developers, threat hunters, and blue team analysts who want to understand how real-world malware techniques work in practice. It is also useful for ethical hackers and cybersecurity students seeking hands-on experience with malware concepts across Windows, Linux, macOS, Android, and iOS in controlled lab environments. Familiarity with C/C++, basic Assembly, operating system internals, and core cybersecurity concepts will help readers get the most from the examples. Table of Contents - Malware Families and Capabilities for Windows - Exploring Malware Running Techniques for Windows - Windows Malware Persistence Mechanisms - Bypass Windows OS Security and Cat and Mouse Game for Windows - Linux Malware Capabilities - Exploring Malware Running Techniques for Linux - Linux Malware Persistence Mechanisms
Details
- Format
- Paperback
- ISBN-13
- 9781807427597
- Publisher
- Packt Publishing
- Published
- August 31, 2026
- Pages
- 258
- Weight
- 15.8 oz
- Subject
- Computers
Popular in Computers
Browse Computers
The Agi Chronicles: The Inside Story of the Race to Create an Artificial Superintelligence
Kevin Roose
$25.99

AI Engineering: Building Applications with Foundation Models
Chip Huyen
$65.99

If Anyone Builds It, Everyone Dies: Why Superhuman AI Would Kill Us All
Eliezer Yudkowsky
$23.99

Designing Data-Intensive Applications: The Big Ideas Behind Reliable, Scalable, and Maintainable Systems
Martin Kleppmann
$58.99

Build a Large Language Model (from Scratch)
Sebastian Raschka
$65.99

Superintelligence: Paths, Dangers, Strategies
Nick Bostrom
$16.99

Python Crash Course, 3rd Edition: A Hands-On, Project-Based Introduction to Programming
Eric Matthes
$38.99
Build a Reasoning Model (from Scratch)
Sebastian Raschka
$65.99
The Book of Why: The New Science of Cause and Effect
Judea Pearl
$18.99

The AI Con: How to Fight Big Tech's Hype and Create the Future We Want
Emily M. Bender
$25.99

The Linux Command Line, 3rd Edition: A Complete Introduction
William Shotts
$38.99

The God Test: Artificial Intelligence and Our Coming Cosmic Reckoning
Robert Wright
$23.99